
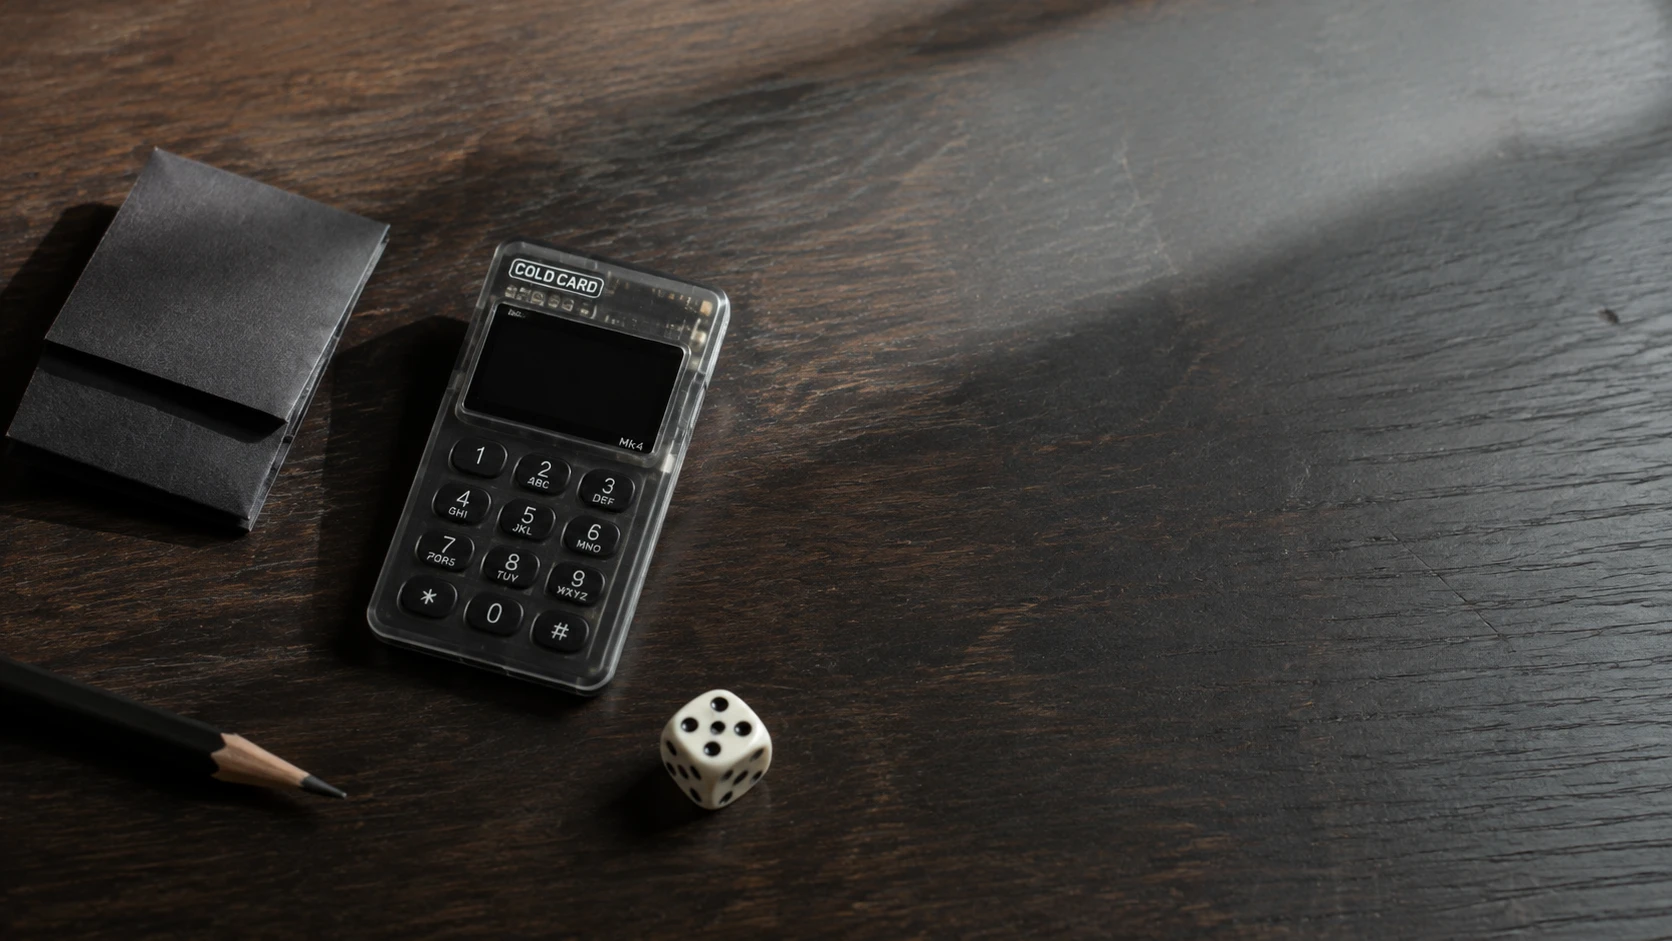
Coldcard is a Bitcoin-only hardware wallet made by Coinkite, a Canadian company. It supports Bitcoin and nothing else — no ETH, no USDT, no other assets — deliberately, to keep the codebase small and the attack surface narrow.
As of August 3, 2026, public on-chain tallies put this incident at roughly 4,585 addresses and about 1,367 BTC stolen, worth around $88.6 million at the time. The attack may still be ongoing, and both the address count and the total may change.
What makes this worth paying attention to: the attacker never touched the hardware wallets and never needed anyone to click a phishing link. They exploited weak randomness to brute-force seeds on their own machines, derived the private keys, and moved the funds.
Who is affected
Coldcard users tend to take security seriously. They don’t leave coins sitting on exchanges, they insist on holding their own keys, and they steer clear of the extra risk that comes with smart contracts, DeFi and altcoins.
But this time the problem was in the most basic step of all: the randomness used when the wallet generated the seed wasn’t as strong as it needed to be. A device that has never been online and a seed phrase that has never leaked don’t guarantee your funds are safe. One victim who had held 18.25 BTC for eight years lost all of it within minutes.
Per Coinkite’s security advisory, the affected range covers:
- Mk2 and Mk3, firmware 4.0.1 through 4.1.9;
- Mk4 and Mk5, versions before 5.6.0;
- Q, versions before 1.5.0Q;
- certain Edge firmware versions.
Mk2 and Mk3 are the worst affected. Mk4, Mk5 and Q also mixed in random data from a secure element, which makes attacking them harder, but the seeds they generated still fell short of the intended security strength.
If seed generation included at least 50 independent, secret and fair dice rolls — or if the wallet used a strong and unique BIP-39 passphrase — the risk is much lower. Even so, the official recommendation is that those users migrate to a new seed as soon as they can.
What happened
How the bug got into the firmware
- March 1, 2021: a code change accidentally altered the seed generation path. Instead of using the hardware random number generator as intended, the code fell through to MicroPython’s software pseudo-random fallback.
- March 17, 2021: firmware 4.0.1 shipped, and the bug went out in a release. From then on, seeds generated on affected Mk2 and Mk3 firmware carried only about 40 bits of effective entropy; Mk4, Mk5 and Q around 72 bits — far below the 128 bits they were designed for.
- July 29, 2026: some users found bitcoin moving out of their wallets with no action on their part. A bug that had lain dormant for over five years started causing real losses.
How the attack worked
The attacker moved funds in batches, prioritizing single-signature addresses with large balances and long periods of inactivity. Once swept, the funds were consolidated into attacker-controlled addresses, most of which had not moved on at the time of the tally.
- July 29: some victims reported stolen funds. One user’s 18.25 BTC was moved out within minutes, worth about $1.6 million at the time.
- July 30: early tallies showed about 594 BTC taken from roughly 500 addresses; the scope then widened to 1,196 wallets and about 1,083 BTC.
- July 31: another ~76.16 BTC moved, across roughly 1,478 addresses.
- August 1: another ~207.73 BTC, across roughly 1,912 addresses.
These figures come from public tallies taken at different times using different methods. You can’t just add up every batch and address count. The 1,367 BTC in the headline is an estimate as of publication, not a final loss figure.
How the vulnerability works
Normally a hardware wallet generates a seed from high-quality randomness, then derives the mnemonic, private keys and addresses from it. The space of possible values is far too large to enumerate.
Picture finding one grain of sand. A proper 128-bit random number means searching a range too large to imagine. The Mk2 and Mk3 were left with roughly 40 bits of effective entropy — a search space of around a trillion possibilities. Still enormous to a human, but well within reach of modern hardware doing bulk attempts.
An attacker can pre-generate the candidate seeds, derive the corresponding addresses, and compare them against addresses with balances on chain. When one matches, they have the private key and can sign transactions. The whole thing can be done offline, so the victim never has to connect the device or expose the mnemonic.
AI tools did help researchers locate and reproduce the problem faster. But what actually cost people money wasn’t AI — it was insufficient randomness in seed generation. Given the bug exists, ordinary programs and GPU clusters can do the enumeration just as well.
What to do now
If your seed was generated by an affected Coldcard, don’t just update the firmware and keep using it. An update only ensures new seeds are generated correctly; it cannot repair a weak seed that already exists.
A reasonably careful migration looks like this:
- Download and install the fixed firmware for your model from official sources.
- Generate a brand-new seed on the fixed device, or on another device you trust, and back it up properly.
- Verify the new wallet’s receive address on the device screen.
- Send a small amount first and confirm the new wallet receives and restores correctly.
- Once that checks out, move the rest.
- Only deal with the old seed’s backup after every transaction has confirmed.
Don’t skip address verification, backup verification or the small test transfer in a rush. Mistakes made during migration can cost you faster than the vulnerability itself.
What to take from it
A hardware wallet solves key isolation and transaction signing. It does not remove the trust you place in the device, the firmware, and the seed generation process. A cold wallet that never goes online doesn’t mean every key it generates is strong enough.
If you want to rely less on a single device’s random number generator, you can add dice entropy using the vendor’s documented and verified procedure. The dice results are key material themselves: don’t photograph them, don’t store them online, don’t hand them to software you don’t trust, and don’t assume a couple of casual rolls is enough.
For larger balances, consider multisig: keys generated by different vendors and different implementations, jointly controlling the funds. Even if one device has a flaw, an attacker usually can’t move the assets with a single key. Multisig does add complexity to backup, recovery and daily use, though — so rehearse the recovery flow for real before you rely on it.
This incident is another reminder that self-custody doesn’t end at buying a hardware wallet. A security setup you can actually rely on has to account for seed generation, backup, firmware updates, device isolation and recovery verification together.