
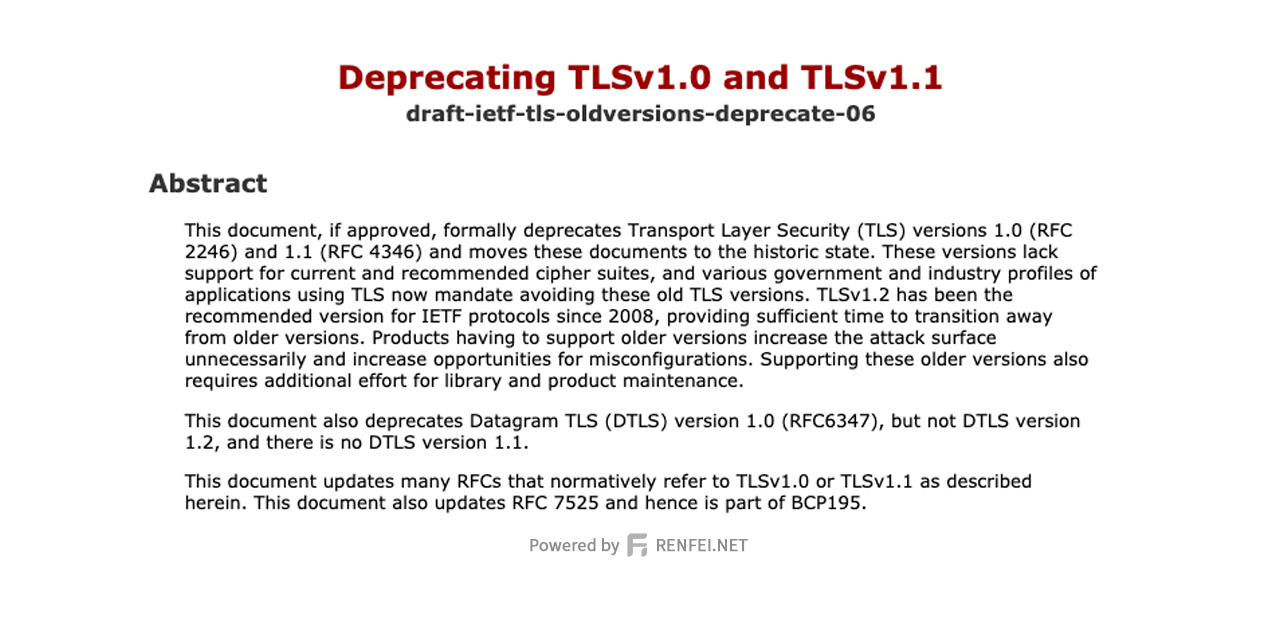
As part of our plan to improve the security of RENFEI.NET, we have stopped supporting Transport Layer Security (TLS) 1.0 and TLS 1.1. RENFEI.NET will refuse TLS 1.0 and TLS 1.1 handshakes, including those for integrations with our various services. Google, Microsoft, Cisco, Apple and Mozilla announced that their browsers and services would stop supporting TLS 1.0 and 1.1 starting March 2020. RENFEI.NET reviewed and carried out the upgrade to the TLS standard carefully, following the industry requirement — the IETF proposal to deprecate these versions.
Please make sure you are using TLS 1.2 or later to avoid interruption accessing or integrating with any RENFEI.NET service. This change affects every connection to RENFEI.NET, including the web and APIs.
The IETF Proposal to Deprecate

The IETF announced that TLS 1.0 (RFC 2246) and TLS 1.1 (RFC 4346) are formally deprecated. These versions lack support for current and recommended cryptographic algorithms and mechanisms.
TLS 1.2 became the IETF-recommended version in 2008 (superseded by TLS 1.3 in 2018), so the IETF considers enough time to have been allowed for users to move off the old versions. Dropping support for them shrinks the attack surface, reduces opportunities for misconfiguration, and simplifies library and product maintenance.
TLS 1.0 shipped in 1999, and nearly two decades later — around 2018 — the IETF began discussing deprecating TLS 1.0 and 1.1. Around that time the major browsers also announced plans to drop TLS 1.0 and 1.1 in 2020.